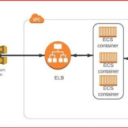
| AWS ECS (Elastic Container Service) is a fully managed container orchestration service that allows you to run and manage Docker containers at scale on AWS. It offers benefits like automated deployments, scaling, load balancing, and security, making it easy to run and manage containerized applications without the complexities of managing infrastructure.
Here's a simple Terraform example to deploy an ECS (Elastic Container Service) cluster on AWS, complete with an ECS cluster, a task definition, and a service running a container. This configuration assumes you have Docker images already available in Amazon ECR (Elastic Container Registry) or another container registry. Example: Simple ECS Cluster and Service This example will: - Create an ECS Cluster.
- Define an ECS Task Definition for a container.
- Launch an ECS Service that will run the container.
Prerequisites Make sure you have the following: - An Amazon ECR repository with a Docker image pushed to it.
- An AWS IAM role with permissions for ECS and EC2 (required for the ECS tasks).
Step 1: Define Variables (variables.tf) Define variables for flexibility. This example assumes the Docker image URI is stored in Amazon ECR. variable "region" {
default = "us-west-2"
description = "AWS region"
}
variable "ecs_cluster_name" {
default = "simple-ecs-cluster"
description = "Name of the ECS cluster"
}
variable "ecr_image_uri" {
description = "ECR URI of the Docker image"
}
variable "task_cpu" {
default = 256
description = "CPU units for the ECS task"
}
variable "task_memory" {
default = 512
description = "Memory for the ECS task"
}
Step 2: Create an ECS Cluster and ECS Service (main.tf) provider "aws" {
region = var.region
}
# ECS Cluster
resource "aws_ecs_cluster" "ecs_cluster" {
name = var.ecs_cluster_name
}
# IAM Role for ECS Task
resource "aws_iam_role" "ecs_task_execution_role" {
name = "ecsTaskExecutionRole"
assume_role_policy = jsonencode({
Version = "2012-10-17",
Statement = [
{
Action = "sts:AssumeRole",
Effect = "Allow",
Principal = {
Service = "ecs-tasks.amazonaws.com"
}
}
]
})
}
resource "aws_iam_role_policy_attachment" "ecs_task_execution_role_policy" {
role = aws_iam_role.ecs_task_execution_role.name
policy_arn = "arn:aws:iam::aws:policy/service-role/AmazonECSTaskExecutionRolePolicy"
}
# ECS Task Definition
resource "aws_ecs_task_definition" "ecs_task" {
family = "simple-task"
cpu = var.task_cpu
memory = var.task_memory
network_mode = "awsvpc"
requires_compatibilities = ["FARGATE"]
execution_role_arn = aws_iam_role.ecs_task_execution_role.arn
container_definitions = jsonencode([{
name = "my-simple-container"
image = var.ecr_image_uri
cpu = var.task_cpu
memory = var.task_memory
essential = true
portMappings = [
{
containerPort = 80
hostPort = 80
protocol = "tcp"
}
]
}])
}
# ECS Service
resource "aws_ecs_service" "ecs_service" {
name = "simple-ecs-service"
cluster = aws_ecs_cluster.ecs_cluster.id
task_definition = aws_ecs_task_definition.ecs_task.arn
desired_count = 1
launch_type = "FARGATE"
network_configuration {
subnets = ["<subnet-id-1>", "<subnet-id-2>"] # Replace with your VPC subnets
security_groups = ["<security-group-id>"] # Replace with a security group that allows inbound traffic
assign_public_ip = true
}
}
Step 3: Provide the terraform.tfvars File Create a terraform.tfvars file to set the values for required variables, especially ecr_image_uri. ecr_image_uri = "YOUR_ECR_IMAGE_URI"
region = "us-west-2"
Step 4: Run Terraform Commands Initialize Terraform: terraform init
Plan the infrastructure: terraform plan
Apply the configuration: terraform apply
Type yes to confirm.
Summary aws_ecs_cluster: Creates the ECS cluster.aws_ecs_task_definition: Defines the Docker container configuration.aws_ecs_service: Runs the task within the ECS cluster using Fargate.
This setup creates a simple ECS service that uses a single container. For production setups, consider load balancers, autoscaling, and additional security configurations. |