Is AWS API Gateway a "Complete" Service That Doesn't Need DR?The short answer is: It is highly available within a single region by default, but it still requires a DR (Disaster Recovery) strategy for multi-region outages.
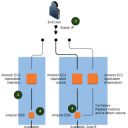
→ It sounds' like almost yes. Regional High Availability (No Configuration Needed)- AWS Managed Multi-AZ: AWS API Gateway is a fully managed service. By default, AWS deploys and replicates API Gateway across multiple Availability Zones (AZs) within a target region.
- Automatic Scaling and Failover: If an entire AZ goes down, AWS automatically routes traffic to healthy AZs. You do not need to configure active-passive or active-active setups within a single region.
Multi-Region Disaster Recovery (User Configuration Required)- Region-Level Outages: While rare, entire AWS regions can experience outages. Because API Gateway is a regional service, a regional failure will take your API down.
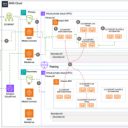
- DR Responsibility: To achieve true DR (Business Continuity), you must design a Multi-Region architecture. This involves deploying API Gateway in two different regions (e.g., us-east-1 and us-west-2) and routing traffic using Amazon Route 53 (using Latency, Failover, or Geolocation routing policies).
What is AWS API Gateway?Amazon API Gateway is a fully managed service that makes it easy for developers to create, publish, maintain, monitor, and secure APIs at any scale. It acts as a "front door" for applications to access data, business logic, or functionality from backend services, such as workloads running on Amazon EC2, code running on AWS Lambda, or any web application. The service handles all the tasks involved in accepting and processing up to hundreds of thousands of concurrent API calls, including traffic management, CORS support, authorization and access control, throttling, monitoring, and API version management. By supporting containerized, serverless, and traditional web workloads, API Gateway simplifies the process of exposing backend functionalities as secure, reliable, and high-performing HTTP, REST, and WebSocket APIs. Why Use AWS API Gateway?AWS API Gateway acts as a "front door" for applications. Instead of exposing your backend servers directly to the internet, API Gateway provides a managed, secure, and scalable entry point. - Full Managed Scalability: It automatically handles hundreds of thousands of concurrent API calls without you having to provision or manage servers.
- Traffic Management & Throttling: You can prevent backend overload by setting rate limits (throttling) and burst limits per API key or client.
- Security & Access Control:
- Integrates out-of-the-box with AWS WAF (Web Application Firewall) to block malicious traffic.
- Supports multiple authorization methods: AWS Cognito, Lambda Authorizers, and IAM.
- API Lifecycle Management: Easily manage different versions and environments of your API (e.g.,
dev, test, prod) using "Stages." - Mocking and Transformation: You can mock API responses for frontend testing before the backend is ready, and transform request/response payloads (XML to JSON, etc.) on the fly.
- Performance (Caching): API Gateway offers built-in caching to reduce the load on your backend and improve response times for duplicate requests.
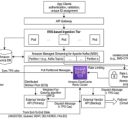
3. Multi-AZ Application Architecture with API GatewayTo integrate AWS API Gateway with a backend application running in a private VPC across Multi-AZ, you should use Private Integration via VPC Link. This keeps your backend secure inside private subnets while allowing API Gateway to route traffic to them. Recommended Architecture Flow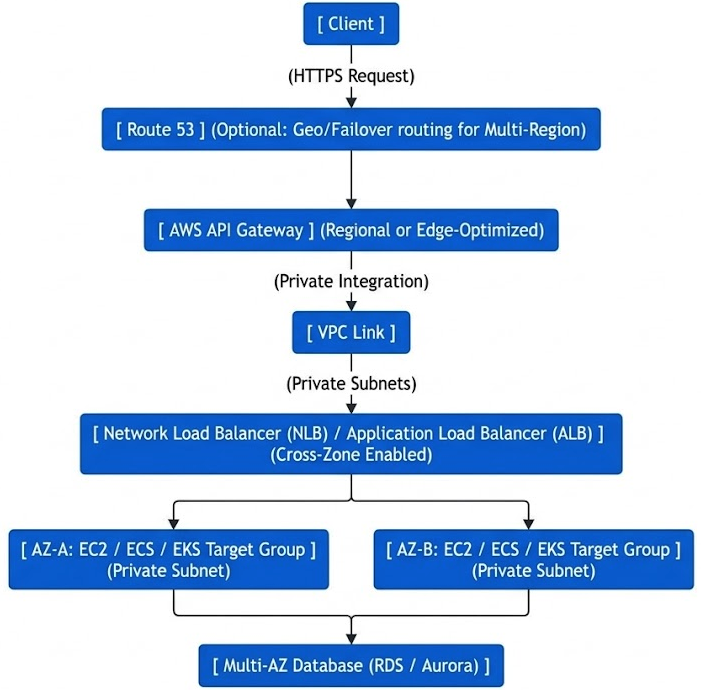
Step-by-Step Architectural Components1. Client to API Gateway: The client sends an HTTPS request to API Gateway (using a custom domain name secured with AWS Certificate Manager).
2. API Gateway to VPC Link: - To access resources inside your private VPC, you configure a VPC Link in API Gateway.
- This creates Elastic Network Interfaces (ENIs) inside your VPC that API Gateway uses to securely tunnel traffic.
3. VPC Link to Load Balancer (Multi-AZ): - The VPC Link points to an Internal ALB (Application Load Balancer) or NLB (Network Load Balancer).
- The Load Balancer must be configured to span across multiple Availability Zones (e.g., Subnet AZ-A and Subnet AZ-B).
4. Load Balancer to Target Groups: - The Load Balancer performs health checks and distributes traffic evenly across target instances (EC2, ECS tasks, or EKS pods) running in multiple private AZ subnets.
- If an application instance in AZ-A fails, the Load Balancer routes all traffic to AZ-B instantly.
5. Database Layer: - The application servers connect to a Multi-AZ database (like Amazon RDS or Aurora), where data is synchronously replicated to a standby instance in a different AZ for seamless database failover.
|